Taming Unbounded Telemetry in Healthtech
Healthtech services, by their nature, handle sensitive data and require robust auditing. However, the sheer volume of telemetry generated can quickly become an unbounded cost and a compliance nightmare. A common challenge is linking security incidents, particularly those involving compromised API keys, back to the specific code and workload responsible. Traditional logging often captures too much or too little, making attribution difficult and potentially exposing secrets in logs, which is a critical security no-go.
The core problem is twofold: accurately identifying the source of a compromised key without logging the key itself, and doing so in a cost-effective, auditable manner. This requires a shift from logging raw secrets to logging immutable identifiers that, when combined, provide a strong signal for attribution. The proposed solution focuses on a single, critical event: the authenticated startup of a service that uses an API key.
Deriving Immutable Fingerprints
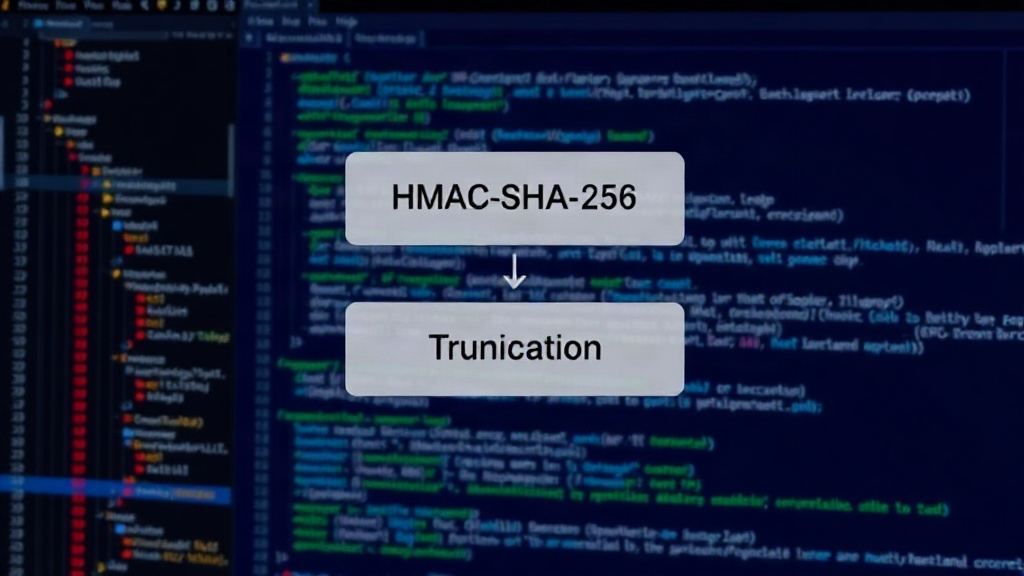
The proposed architecture mandates logging a non-reversible API-key fingerprint. This fingerprint is not derived directly from the key itself, but rather through a cryptographically secure process using HMAC-SHA-256. A dedicated audit key, kept separate from the application's operational keys and log streams, is used for this derivation. The resulting hash is then truncated to a predefined, documented length. This process ensures that the fingerprint is unique to the key and its derivation context but cannot be used to reverse-engineer the original API key or serve as a substitute for it in authentication.
Crucially, this fingerprint is bound to an immutable build identifier, the workload identity (e.g., container ID, service name), and the deployment attempt. This creates a robust chain of evidence. If a credential incident occurs later, this minimal log record allows security teams to pinpoint the exact code version, the specific running instance, and the deployment context that was active when the API key was in use. This is a stark contrast to logging the API key itself, which violates OWASP secrets guidance and creates significant security risks.
Preventing Audit Trail Bloat
A key architectural constraint is the prevention of the audit trail from becoming another unbounded telemetry bill. This is achieved through two primary mechanisms: a uniqueness constraint and a narrow retention policy. The uniqueness constraint ensures that for a given service startup event, only one such record is created. This prevents redundant data from being logged if a service restarts multiple times within a short period or if identical workloads are spun up concurrently without distinct identities.
The narrow retention policy is equally critical. Instead of retaining audit logs indefinitely, they are kept for a limited, documented period. This period should be sufficient for incident response and forensic analysis but short enough to prevent excessive storage costs. This proactive approach to data lifecycle management is essential for services handling large volumes of data or operating under strict cost controls, especially in the healthtech sector where data privacy regulations like HIPAA are paramount.
Attribution in Practice
Consider a health data service that uses an API key to communicate with a third-party analytics provider. Under this new logging strategy, when the service starts, it generates a fingerprint of its API key using the HMAC-SHA-256 process with the separate audit key. This fingerprint, along with the immutable build ID of the deployed code, the container ID running the service, and a timestamp of the deployment attempt, is logged. The actual API key is never written to the logs.
Months later, a security alert indicates that the API key used for the analytics provider has been compromised and is being used maliciously. With the proposed logging mechanism, the security team can query the audit logs. They would look for records associated with the compromised API key's fingerprint. The immutable identifiers in those logs would immediately point to the specific version of the health data service's code, the exact container instance that was running, and the deployment it belonged to. This allows for rapid containment, forensic investigation into that specific workload and code version, and a clear understanding of the potential blast radius, all without having exposed the sensitive API key in the logs.
The Unanswered Question: Key Rotation Impact
While this method provides excellent attribution for incidents tied to a specific key's usage, what remains unaddressed is the precise operational overhead and potential edge cases during API key rotation. If an API key is rotated frequently, does the process of generating and logging the fingerprint introduce latency that could impact service startup times? Furthermore, how does the system handle scenarios where a key is rotated mid-deployment or when multiple keys are active for a single service instance during a transition period? The current proposal focuses on a single authenticated startup event, but real-world scenarios might demand more nuanced handling of dynamic credential management.
Broader Implications for Healthtech Security
This approach offers a tangible solution to a common, costly problem in cloud-native environments, particularly for regulated industries like healthtech. By focusing on immutable identifiers and cryptographically derived fingerprints, it balances security requirements with operational realities. It moves away from the tempting but dangerous practice of logging secrets and towards a more sophisticated, attribution-focused logging strategy. The emphasis on a narrow retention policy and uniqueness constraints directly addresses the spiraling costs associated with telemetry, making robust auditing accessible even for startups with limited budgets. This could set a new standard for secure and cost-effective logging in sensitive data environments.