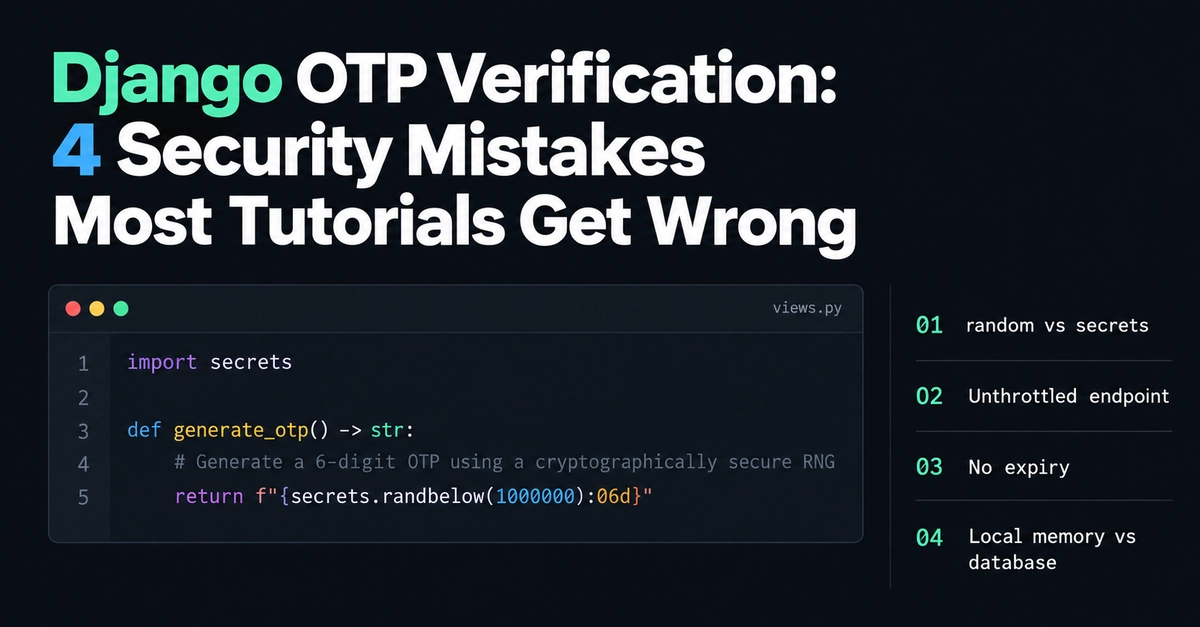
The Naive OTP Flow
Many Django tutorials demonstrate One-Time Password (OTP) verification using a straightforward approach. A typical implementation involves generating a random six-digit number, storing it directly in the user model, and then comparing it against user input. The code often looks like this:
otp
user.otp_code = otp
user.save()
This method appears functional during local development. However, it harbors four critical security flaws that become apparent only under real-world conditions, especially with multiple servers and malicious actors.
Mistake 1: Storing OTP Directly in the User Model
The most common oversight is storing the OTP code directly as a field on the user model. While convenient for local testing, this practice creates a significant security vulnerability. If an attacker gains even limited access to your database (e.g., through a SQL injection vulnerability or compromised credentials), they can potentially read all active OTP codes for all users. This allows them to intercept verification flows and impersonate users. Furthermore, storing sensitive, time-limited codes directly alongside user profile data can lead to data leakage if database access controls are not meticulously managed. Think of it like writing down your PIN number on the back of your ATM card; it defeats the purpose of the PIN.
Mistake 2: Using a Predictable OTP Generation Method
Another frequent error is the use of predictable methods for OTP generation. While `random.randint(100000, 999999)` might seem sufficient, it's not cryptographically secure. Standard pseudo-random number generators (PRNGs) can produce sequences that are predictable if an attacker knows the seed or can observe enough generated numbers. In a multi-server environment, especially if servers share a common clock or are synchronized, an attacker could potentially guess active OTP codes. A more robust approach involves using a cryptographically secure pseudo-random number generator (CSPRNG) like Python's `secrets` module. This ensures that each generated OTP is truly unpredictable, making it significantly harder for an attacker to guess valid codes.
Mistake 3: OTPs That Don't Expire
Many tutorials fail to implement an expiration mechanism for OTPs. An OTP is designed to be valid for a very short period. Without an expiration, a previously generated OTP could remain valid indefinitely. If an attacker obtains an OTP (even through a legitimate but delayed channel, like a slow email server), they could use it later to compromise an account. This also exacerbates the problem of predictable generation; if an OTP doesn't expire, an attacker has more time to guess or brute-force it. Implementing a time-based expiry, typically 5-15 minutes, is crucial. This often involves adding a timestamp to the OTP record and checking it during verification.
Mistake 4: Storing OTPs in Plain Text in the Database
This mistake is a direct consequence of the first one and deserves separate mention. Storing OTPs in plain text in the database, even if on a separate table, is highly risky. While not as bad as storing them directly on the user model, it still means that a database breach would expose all active OTPs. For enhanced security, OTPs should be treated like passwords. They should be stored securely, ideally hashed using a strong, salted hashing algorithm (like bcrypt or Argon2). However, hashing OTPs presents a challenge: they are meant to be compared against user input, which is also in plain text. A common pattern is to generate a unique, time-bound token that is stored hashed, and then compare the user-provided token against this hash. Alternatively, some systems opt for shorter-lived, unhashed OTPs with very strict expiration policies, relying on the short lifespan to mitigate risk, but this is less ideal than hashing or using secure tokens.
Beyond the Tutorials: Building Secure OTP
Securing OTP verification requires a layered approach. This means moving beyond basic tutorial implementations. Developers need to consider:
- Secure Storage: Use dedicated, temporary storage for OTPs, separate from user profiles. This could be a cache like Redis with TTL (Time To Live) or a dedicated database table with strict access controls and automatic cleanup.
- Cryptographically Secure Generation: Always use a CSPRNG (e.g., Python's
secretsmodule) for OTP generation. - Strict Expiration: Implement a short, mandatory expiration time for all OTPs.
- Rate Limiting: Protect against brute-force attacks by limiting the number of OTP attempts per user and per IP address within a given timeframe.
- Secure Transmission: Ensure OTPs are sent over secure channels (HTTPS for web, TLS for APIs). For SMS, be aware of SIM swapping risks.
- Auditing: Log OTP generation, delivery, and verification attempts for security monitoring.
By addressing these four common mistakes and implementing these best practices, Django developers can build far more robust and secure OTP verification systems, protecting both their users and their applications from common attack vectors.