The Limits of Automated Reconnaissance
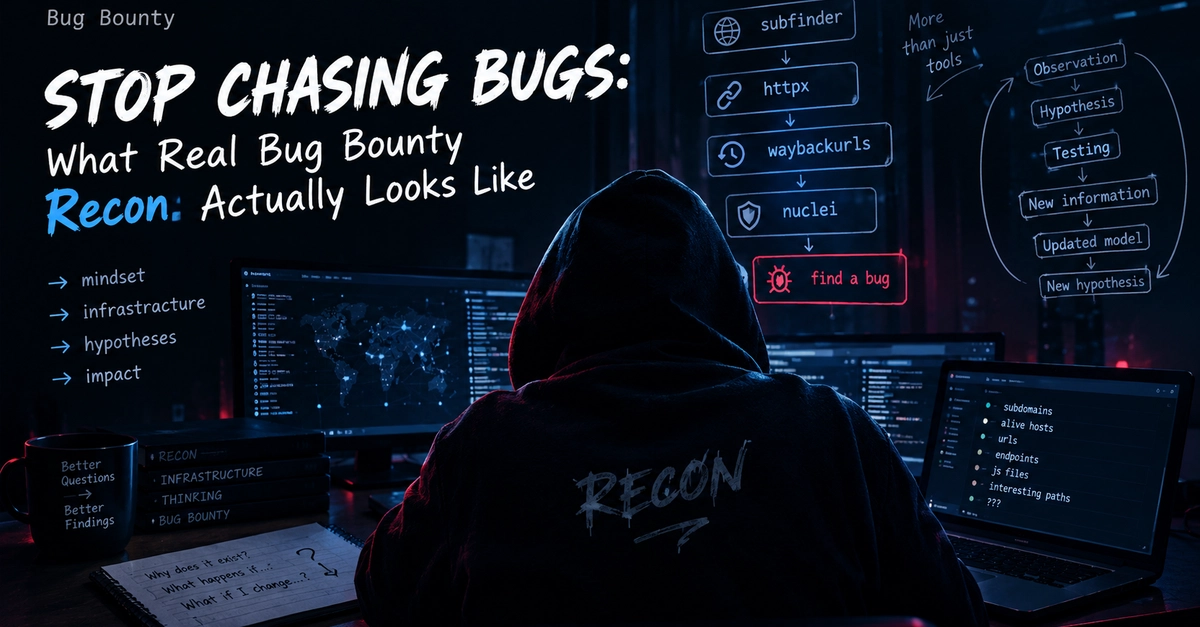
Many bug bounty reconnaissance guides follow a predictable pattern. They emphasize tools like Subfinder and recommend a workflow: gather subdomains, scan them, and repeat. This approach is undeniably useful for asset discovery. Automation helps cast a wide net, identifying a large number of potential targets quickly. Tools can enumerate subdomains, map network topologies, and even perform initial vulnerability scans. However, after extensive engagement with bug bounty programs, a critical realization emerges: the sheer volume of discovered assets is rarely the bottleneck. The real challenge lies not in finding more URLs, but in discerning which of those URLs warrant deeper investigation. The difficulty shifts from quantity to quality, from broad enumeration to focused analysis.
This isn't to dismiss the value of automated tools. They are foundational. Think of them as a high-powered telescope that can scan the entire night sky. You can see countless stars, galaxies, and nebulae. But without an astronomer's knowledge, knowing which celestial body is most interesting, potentially harboring new discoveries, or exhibiting unusual phenomena, is impossible. Automated tools provide the raw data; a human mindset provides the critical evaluation.
Shifting from Quantity to Quality: The Human Element
The core of effective bug bounty reconnaissance is developing a mindset that prioritizes intelligent triage. This means asking the right questions about each discovered asset. Is this subdomain actively served or is it an abandoned artifact? Does this endpoint handle sensitive user data? Are there any unique technologies or frameworks in use that might present novel attack vectors? The ability to answer these questions quickly and accurately separates successful hunters from those who get lost in the noise of vast asset lists.
This shift in focus requires moving beyond the mechanical application of tools. It demands an understanding of web technologies, common misconfigurations, and the typical attack surfaces of various applications and services. A hunter needs to develop an intuition for what looks 'interesting' – not just technically unique, but potentially exploitable. This often involves looking for assets that are:
- Externally facing and actively maintained: Old, unservenk or development subdomains are less likely to yield critical vulnerabilities.
- Handling sensitive information: User credentials, PII, financial data, or internal administrative functions are prime targets.
- Using custom or complex logic: Off-the-shelf solutions are often well-hardened. Bespoke applications or integrations can hide unique flaws.
- Associated with critical business functions: Disrupting or compromising core operations can lead to higher impact findings.
Consider a scenario where an automated tool discovers hundreds of subdomains for a large e-commerce platform. A naive approach would be to scan all of them for common vulnerabilities. A more effective approach involves filtering. Does `dev.api.example.com` handle payment processing? Probably not. Does `admin.example.com` offer a login portal that looks like it's running an outdated version of a known CMS? That's a much higher priority target.
Developing the 'Investigative' Mindset
Cultivating this investigative mindset is an ongoing process. It involves continuous learning and adaptation. Here are key components:
1. Deep Technology Familiarity
Understanding the underlying technologies is paramount. Knowing how common web servers (Nginx, Apache), application frameworks (React, Angular, Django, Ruby on Rails), and backend languages (Python, Java, Node.js) behave, and their common vulnerabilities, allows for more targeted reconnaissance. When you see a specific version of a technology, you immediately know potential weaknesses to probe.
2. Understanding Business Logic
Attackers often exploit flaws in how an application is designed to function, not just technical vulnerabilities. Understanding the intended business logic of an application – how users interact with it, what actions are permitted, and what data is exchanged – is crucial for finding vulnerabilities that automated scanners miss. This might involve analyzing user workflows, identifying authorization bypasses, or finding ways to manipulate application state.
3. Threat Modeling Awareness
Thinking like an attacker means anticipating potential threats. What are the most valuable assets? What are the easiest ways to compromise them? What security controls are likely in place, and where are they weakest? Applying basic threat modeling principles to discovered assets helps prioritize efforts towards areas with the highest potential impact.
4. Iterative Refinement
Reconnaissance isn't a one-time event. It's an iterative process. Initial findings might lead to new questions and new avenues of exploration. A vulnerability found in one area might suggest similar vulnerabilities exist elsewhere. Continuously refining your understanding of the target based on new information is key.
The Role of Tools in an Intelligent Workflow
Tools like Subfinder, Assetfinder, Amass, Nuclei, and Burp Suite remain indispensable. They are the instruments that enable efficient information gathering at scale. However, their output is only as valuable as the interpretation applied to it. The goal is not to replace these tools, but to augment them with human intelligence. A skilled bug bounty hunter uses these tools to automate the tedious parts of data collection, freeing up cognitive resources for critical analysis and creative exploitation. The tool finds the forest; the hunter decides which trees to climb.
The true differentiator in bug bounty reconnaissance is the ability to look beyond the raw list of discovered assets and identify the 'low-hanging fruit' and the 'high-impact targets' that others might overlook. It’s about developing an educated intuition, a critical eye, and a strategic approach that complements, rather than competes with, the power of automation.