The Shifting Landscape of Browser Fingerprinting
Browser fingerprinting, a technique used to identify and track users by collecting unique browser and device characteristics, is undergoing a significant transformation in 2026. While the core concept remains viable, the efficacy of traditional methods has been severely curtailed by privacy-focused initiatives from major browser vendors and the advancement of spoofing techniques. Chrome's Privacy Sandbox, Firefox's noise injection, Safari's API restrictions, and Brave's outright blocking have systematically dismantled many of the signals fingerprinting libraries relied upon. Concurrently, headless browser frameworks have become adept at mimicking legitimate user activity, further complicating identification efforts.
A crucial caveat for anyone operating fingerprinting systems: a fingerprint is not a durable cross-browser identity. No single fingerprint should be treated as definitive proof of a human visitor or an automated bot. The landscape has evolved from a broad collection of easily accessible data points to a more nuanced, and often less reliable, interplay of remaining signals and sophisticated evasion tactics.
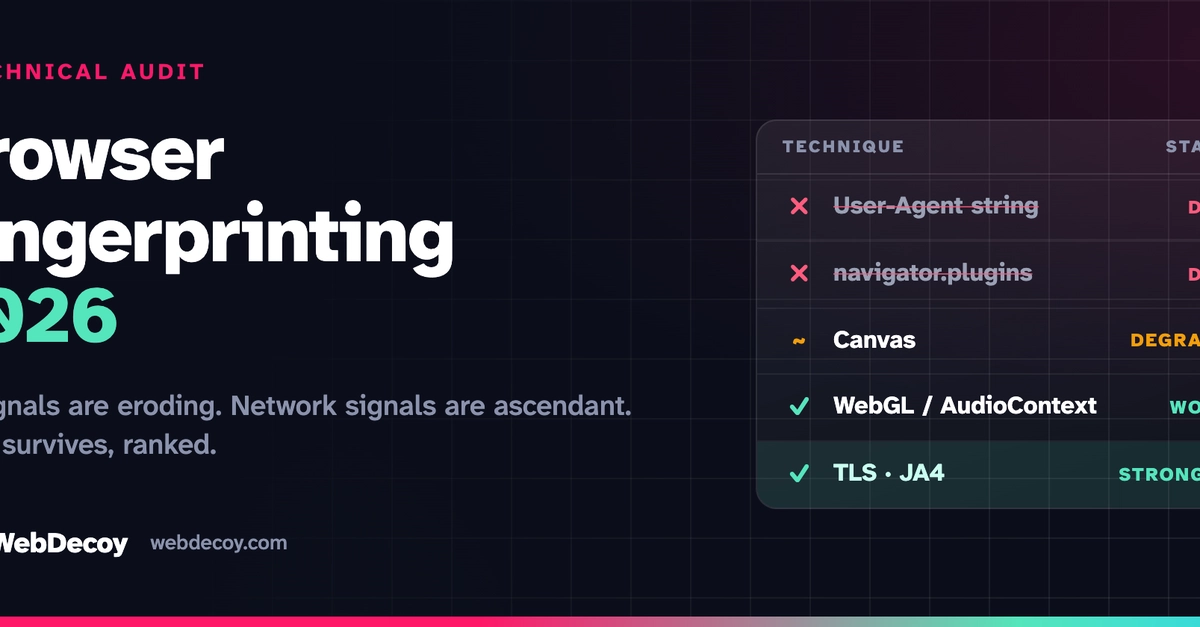
The Signal Scoreboard: What's Working, What's Not
The effectiveness of fingerprinting techniques is best understood by examining their entropy—the amount of unique information they provide—and their resilience against modern defenses. Many formerly high-entropy signals have been neutralized or significantly degraded.
Degraded and Neutralized Signals
Canvas Fingerprinting: Once a cornerstone of fingerprinting, canvas fingerprinting relies on the browser's ability to render specific graphics and text. Subtle differences in GPU, graphics drivers, and font rendering can produce unique outputs. However, browsers have introduced methods to standardize canvas output or inject noise, significantly reducing its entropy. While it might still contribute a small amount of signal, it's no longer the reliable identifier it once was.
WebGL Fingerprinting: Similar to canvas, WebGL fingerprinting leverages graphics rendering capabilities. It examines differences in GPU model, driver versions, and supported extensions. While still potent in some scenarios, browsers are increasingly anonymizing WebGL parameters or limiting access to precise information. The effort required to extract meaningful entropy has increased, and the reliability has decreased.
Font Enumeration: The list of installed fonts on a user's system was a rich source of identifying data. Browsers have largely restricted direct access to this information. While techniques like rendering text to a canvas with specific fonts can still infer font presence, the ability to get a comprehensive, direct list has been removed.
Audio Fingerprinting: This technique analyzes the unique characteristics of a device's audio stack and hardware. Differences in audio codecs, processing, and hardware can lead to distinct fingerprints. However, like other hardware-dependent signals, audio fingerprinting is becoming more susceptible to browser-level noise injection and standardization efforts.
Hardware Concurrency and Device Memory: Information about the number of CPU cores or the amount of RAM was once easily accessible. These metrics are now heavily restricted by browser APIs, as they can contribute to uniquely identifying a device. Their utility has diminished significantly.
Signals with Lingering Utility
User Agent String: While often considered a basic identifier, the User Agent string still provides essential information about the browser, OS, and version. Although it can be spoofed, it remains a foundational element in many fingerprinting attempts, especially when combined with other signals. Privacy enhancements have made it less unique, but not entirely useless.
Screen Resolution and Color Depth: These are relatively stable and easily accessible properties of a user's display. While not highly unique on their own, they contribute to the overall fingerprint, especially in less privacy-hardened browsers.
HTTP Headers: Headers like `Accept-Language` and `Accept-Encoding` can offer clues about a user's preferences and system configuration. While these are generally not high-entropy, they add to the overall picture.
Browser Plugins/Extensions (Limited): Direct enumeration of plugins has been largely curtailed. However, some indirect methods or checking for the presence of specific, widely used extensions might still yield limited signal, though this is rapidly becoming less effective.
Emerging and Evolving Techniques
Headless Browser Spoofing: The most significant development is the sophistication of headless browser frameworks (e.g., Puppeteer, Playwright). These tools can now mimic many of the remaining fingerprintable characteristics of real browsers with remarkable accuracy. They can randomize User Agent strings, spoof canvas outputs, and simulate realistic rendering behaviors, making it harder to distinguish automated traffic from human users based solely on traditional fingerprinting.
Behavioral Analysis: As static fingerprinting signals weaken, behavioral analysis is gaining prominence. This involves observing user interactions: mouse movements, typing speed, scrolling patterns, navigation paths, and time spent on pages. These dynamic, human-like behaviors are much harder to replicate convincingly by bots and offer a more robust signal for distinguishing humans from bots. This shifts the focus from what a browser *is* to how a user *acts*.
Timing Attacks and JavaScript Execution: Subtle differences in how JavaScript executes, the timing of API calls, and network latency can sometimes be exploited to infer unique characteristics of a device or network environment. These are complex and often require advanced techniques but can yield signal where direct data collection is blocked.
WebRTC Leaks: While not strictly a fingerprinting technique, WebRTC can inadvertently reveal a user's local IP address, which can be correlated with other data points. Browsers are improving controls over WebRTC, but leaks can still occur.
The Future: A Cat-and-Mouse Game
The trend is clear: browser fingerprinting is becoming less about collecting a vast array of passive identifiers and more about sophisticated behavioral analysis and exploiting the residual signals that remain. Browser vendors are actively working to close these gaps, leading to a continuous arms race. For developers and security professionals, this means that relying on static fingerprinting alone is a losing strategy. Adaptability, a focus on behavioral biometrics, and a deep understanding of current browser privacy features are essential.
What remains unaddressed is the long-term impact on legitimate privacy-preserving technologies that might inadvertently share characteristics with bot traffic, and how to effectively balance user privacy with the need for security and fraud prevention in this evolving landscape.